Trusted by
We develop, assess, modernise, secure and run platforms on AWS, GCP and Azure. AI-native from analysis through delivery. Fixed scope, fixed timeline, guaranteed deliverables.
AI inferences a day in TrueClaim's claims pipeline
Exam-day traffic surges absorbed for Mereos
Years of engineering experience
Technology companies helped
AI made building fast. It did not make the judgement that decides what to build, what will break under real traffic, or which of its own confident answers is wrong. That comes from having done this many times over, in the years when there was no AI to write the first draft.
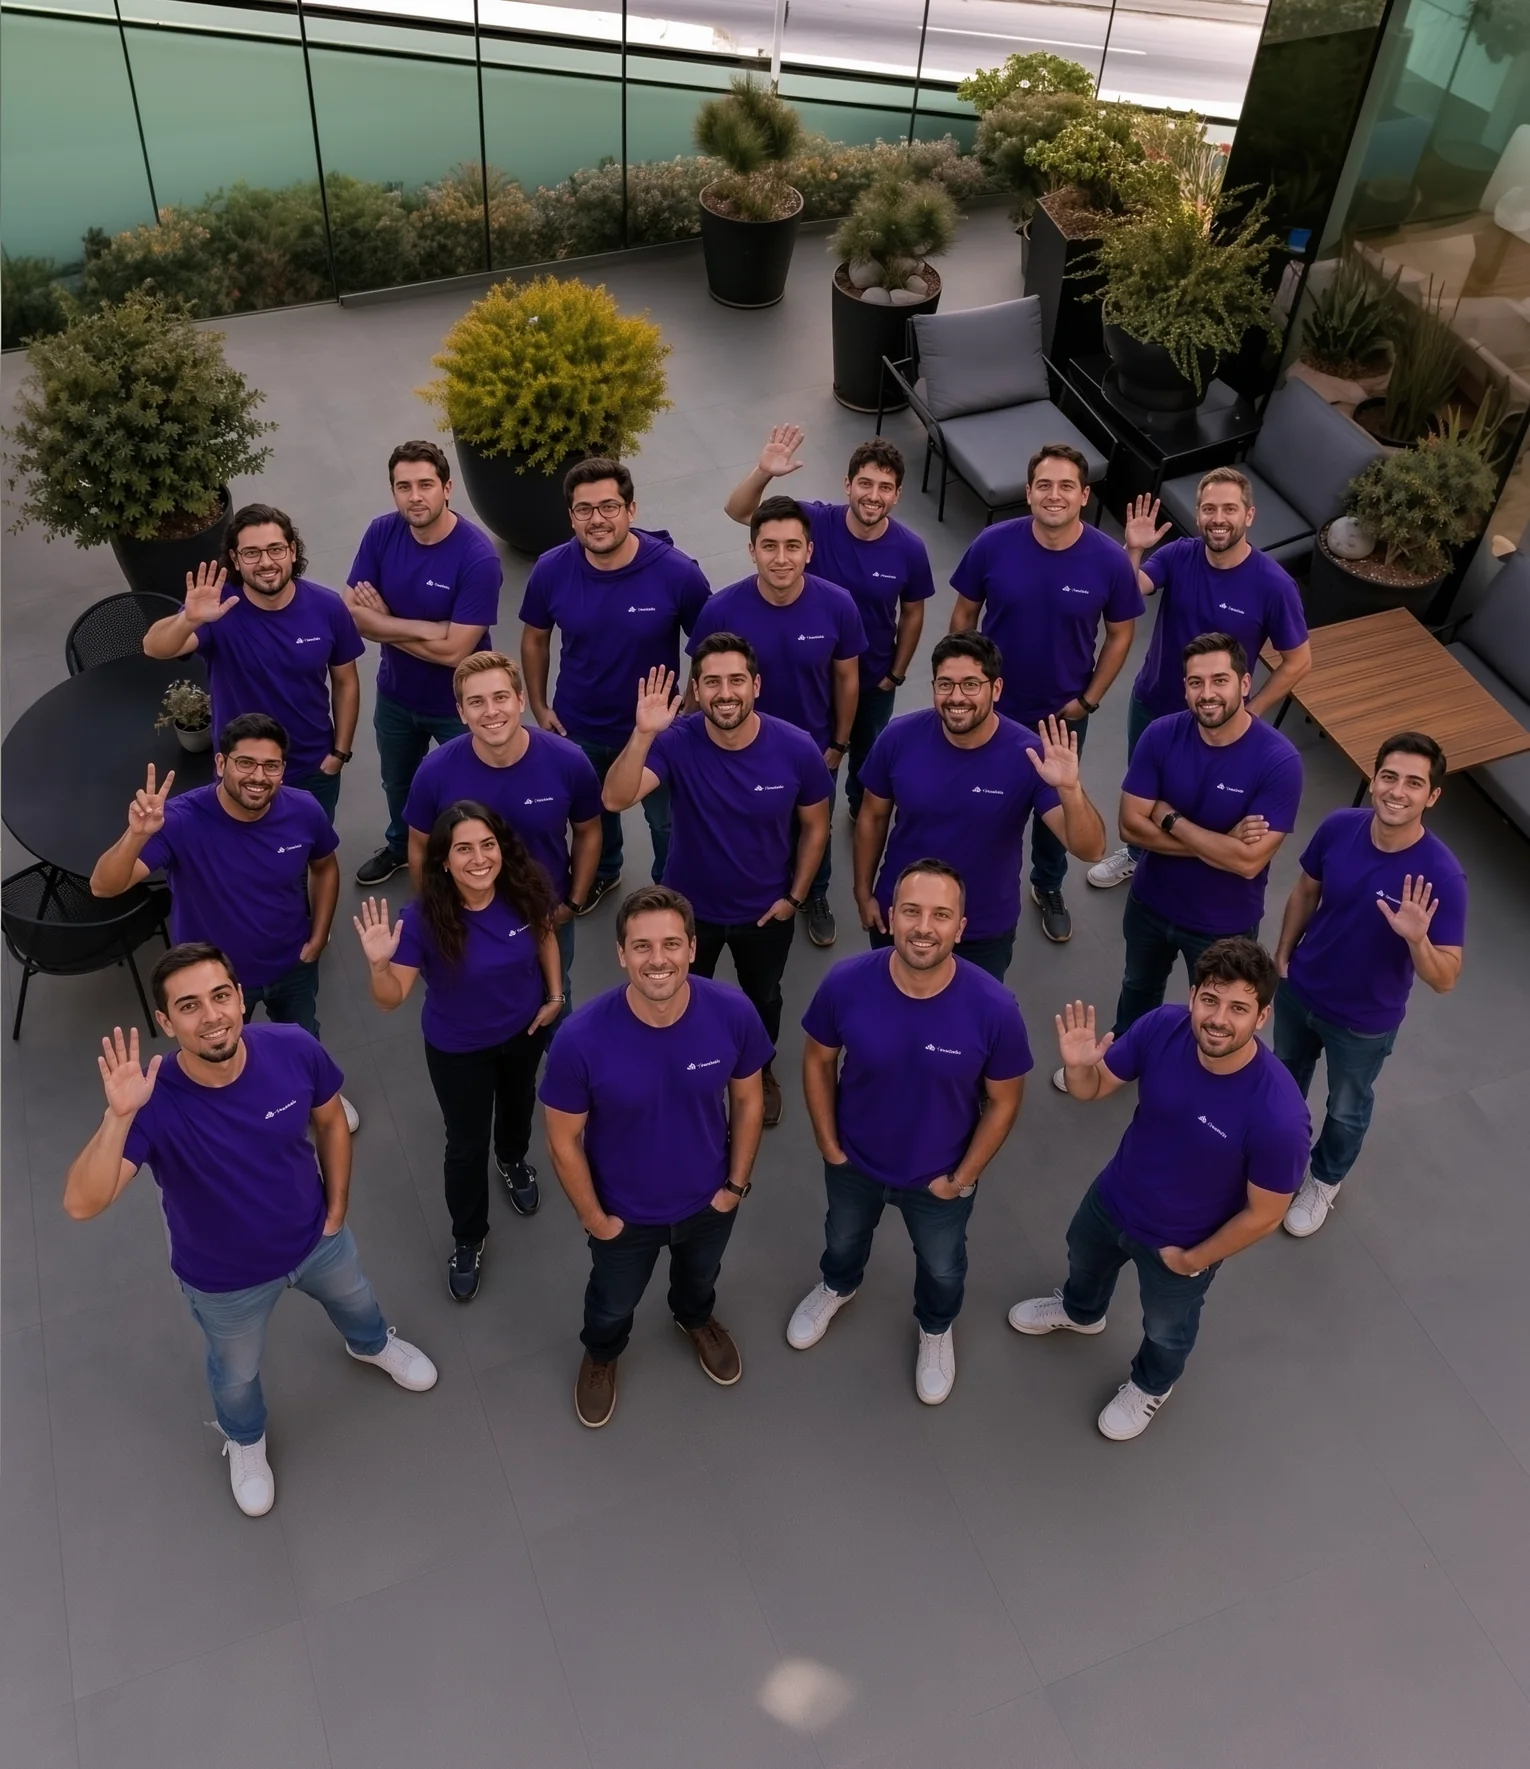
A boutique team of about fifteen, working across the United States, Uruguay and Argentina. Small is the point: the person who scopes your engagement is the person who does it.
Our Partners

Most engagements start in one of four places: building an AI product, getting a platform ready for what is coming, passing an audit, or making sure it scales without going down.
We design and build the systems behind AI products: retrieval, model serving, evaluation, and the infrastructure that carries a prototype to real traffic. The demo is the easy part.
A fixed-scope review of what you already run: what will break, what it is costing you, and what to fix first. We guarantee the deliverable, not an outcome outside our control.
Gap assessment, controls and the evidence trail, so the audit is a formality rather than a scramble. The deliverable is the roadmap and the artefacts, not the auditor's verdict.
A dedicated AI cloud engineer that knows your environment and resolves issues before they become incidents. This is the part that does not finish, and the part that keeps the rest true.
Recognized for machine learning expertise, applied to real-world cloud engineering and infrastructure optimization.
A selection of engagements. Every company below agreed to be named, and the words are theirs.
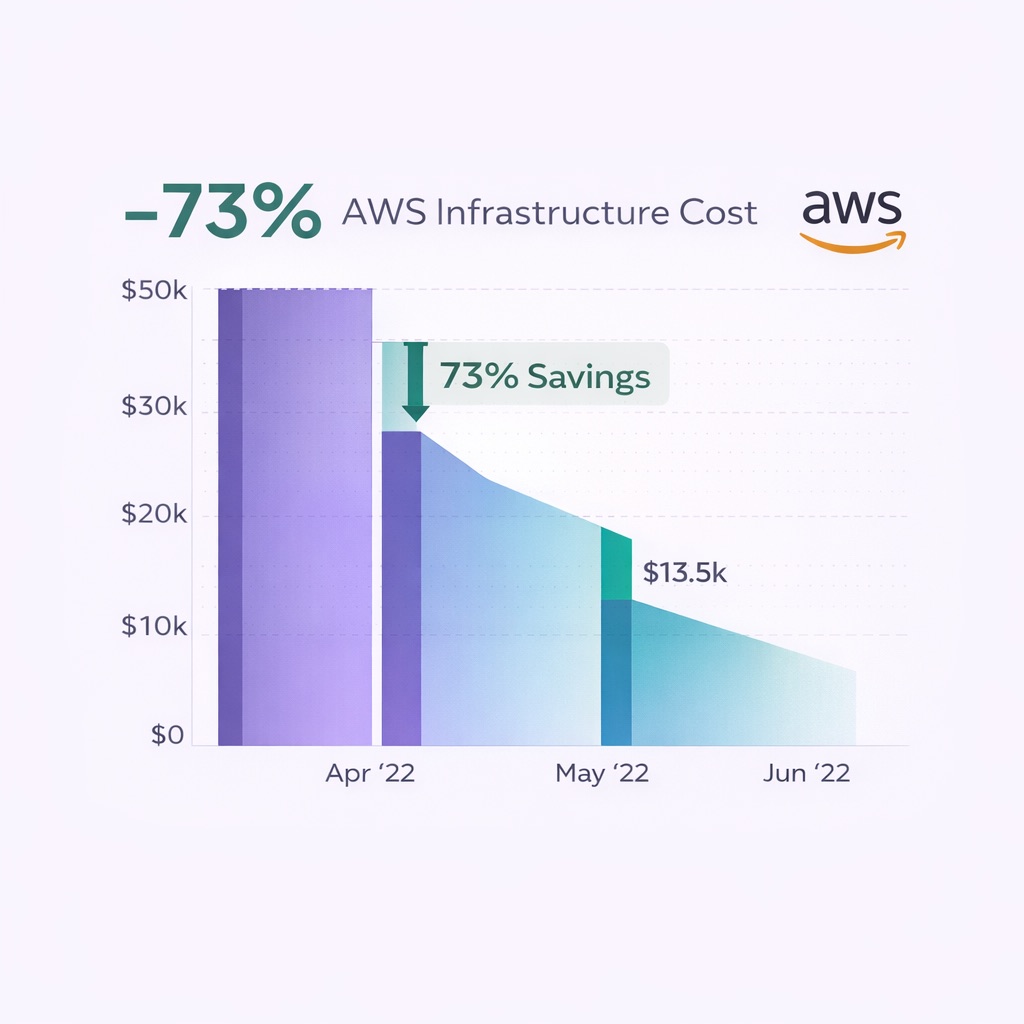
reduction in AWS infrastructure costs
"Not only did they reduce our infrastructure costs by a staggering 73%, but they also helped us modernize our applications and streamline our system. Their three-step process was both effective and tailored to our specific needs."
SOC 2 readiness end to end: controls on Azure, policies, evidence, and the audit itself, renewed cleanly year after year.
From a first gap assessment to a point-in-time Type I, then a clean Type II at the end of the observation period.
Consolidated multiple cloud platforms into AWS with robust security measures for Canadian data regulations.
Became the exclusive partner for deploying government solutions in the cloud with enterprise-grade security.
Infrastructure and DevOps optimization ensuring seamless performance during high-traffic periods for church partners.
Designed and implemented a scalable, secure architecture leveraging cutting-edge AI for assessment integrity.
Built a scalable, secure cloud solution integrating Amazon SageMaker to revolutionize insurance appraisal.
Automated environment delivery and cut infrastructure costs by 25% (up to $300,000 a year) while keeping EKS clusters current.
Moved a coupled EC2 stack to serverless microservices, with encryption throughout and MediaConvert for video at scale.
SOC 2 readiness across an AWS and SageMaker stack, with the ML team approving decisions instead of chasing screenshots.
Thirty minutes to understand your environment and what is pressing. Free, and it ends with a straight answer about whether we are a fit.
One to two weeks, fixed price. You get findings, risks and a prioritised roadmap you could hand to any team, including one that is not us.
If you want us to do the work, our engineers implement it in your environment. Real infrastructure, not a slide deck.
Cost, reliability and security are not projects that finish. Most clients keep us on for the operations, monitoring and reviews that follow.
A green check on a pipeline means every step that ran, succeeded. It does not mean the steps you cared about ran at all.
A marketing site and a blog usually live in different systems, and the join between them is where things quietly rot…
A long-lived access key in CI is a credential you cannot see being used, cannot scope tightly, and will forget to…
Book a 30-minute call. Tell us what you're dealing with and we'll tell you straight whether we can help, and what it would take.
No strings attached.
Prefer email? hello@cloudacio.com